Software supply chain security · Since 2019
Shared worldview for every team.
Reliza builds tooling and delivers services that give security, engineering, product and leadership a single trustworthy view of what they ship, what it contains, and whether it's safe and compliant.
How Reliza tooling fits your supply chain
- SBOM / xBOMYOUR BUILDS
- EnrichBEAR
- ReleaseReARM
- PublishReARM · Oolong
- ConsumeReARM · TEA
Our products
01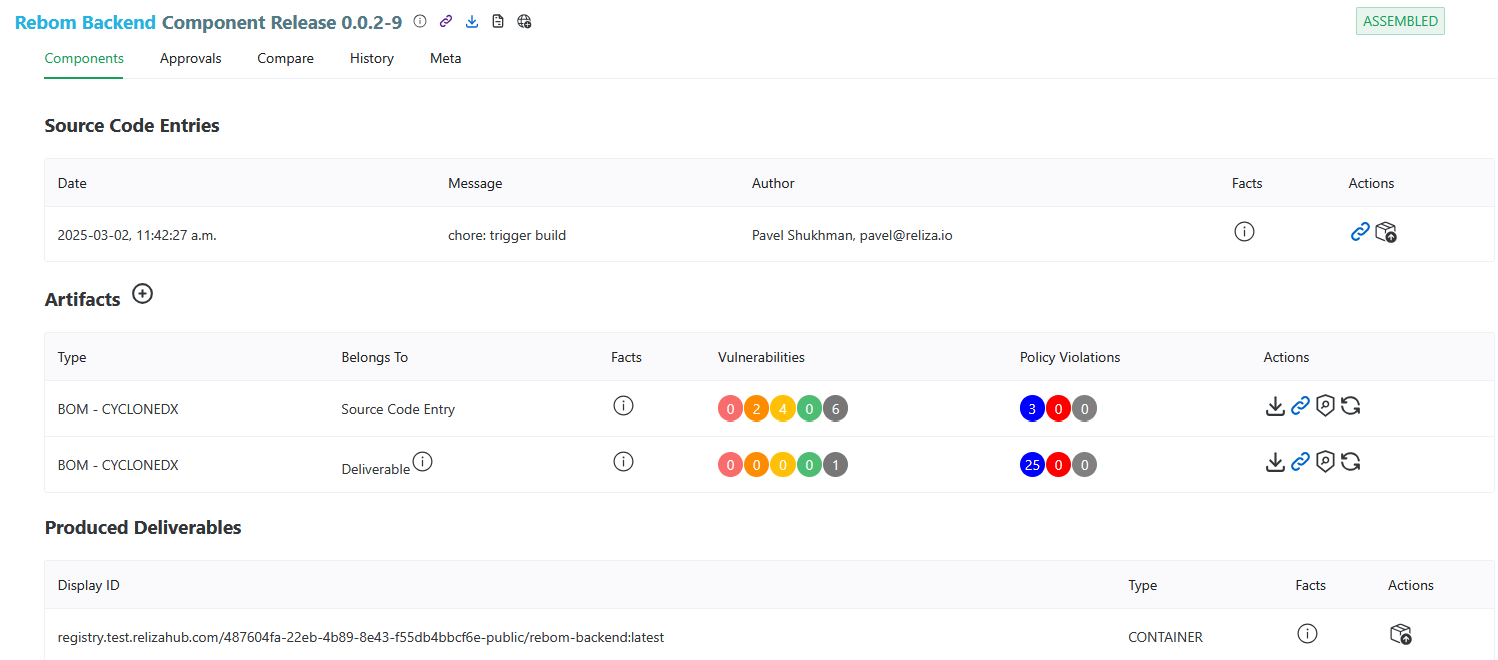 ↳ rearmhq.com
ReARM
RELEASE GOVERNANCE PLATFORMWhat's in every release, whether it's cleared to ship, and the evidence proving both.
02 ↳ GitHub
Oolong
OPEN SOURCE · TEAA lightweight Transparency Exchange API implementation to publish and discover xBOMs.
03 ↳ GitHub
BEAR
OPEN SOURCE · AGENTICEnriches sparse SBOMs with supplier, copyright and license data to make them audit-ready.
Our mission
Make the invisible visible, for everyone in the organization.
Software supply chains are complex. Regulations are tightening. Security incidents are escalating. Yet most organizations still lack a unified view of what they ship. From artifact collection and versioning to compliance dashboards and SBOM transparency, we close that gap.
REGULATIONSEU CRANIS2DORAUS EO 14028 / 14144FDA 524BRBI / SEBI
Services
Hands-on help, by us or with partners.
Transparency Exchange APIECMA TC54-TG1
CycloneDXECMA-424
Authoritative Guide to AI/ML-BOMOWASP · CYCLONEDX
OpenSSF SBOM groupOPEN SOURCE SECURITY FOUNDATION
Clients and Partners